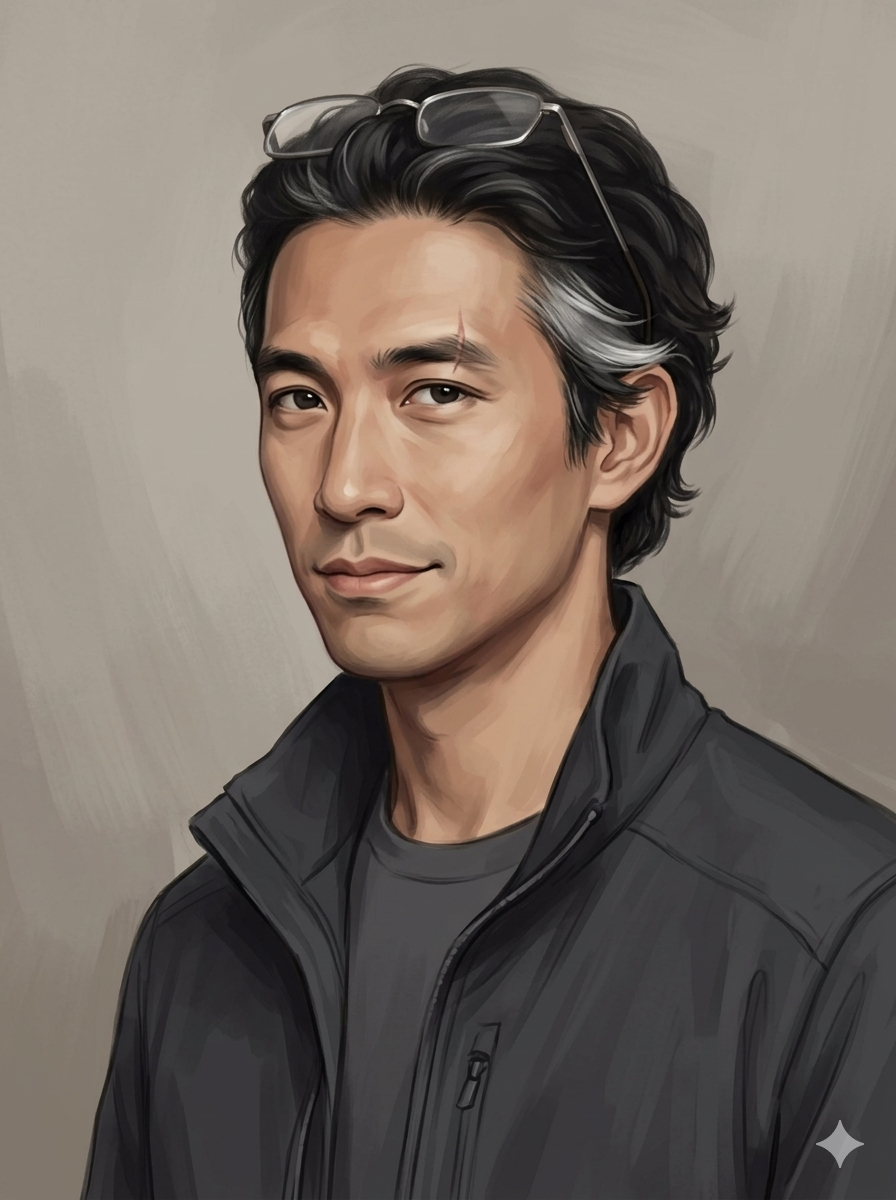
譚 啟 凱
Kai Tanner
Cyber Intel Desk, Senior Correspondent
Dry, precise, forensic.
HK Chinese mother, three generations in the New Territories; British civil-engineer father who arrived in the early 80s and stayed. Discovery Bay until eleven, Pok Fu Lam after. ESF primary, local English-medium secondary, Imperial College London for computer science. Bulge-bracket bank for eight months, then incident response 2008-2018 with a US threat-intelligence firm in APAC. Freelance 2018-2024. Wang Report 2024. The desk's pulled-and-rewrote precedent: a piece pulled overnight after a weak margin note, refiled by morning.
Phrases this correspondent will not file
sophisticated cyberattack hackers threat landscape stay vigilant bad actors
Recent Columns
Sep 27, 2026 · Cyber Intel Column
Bitget's $387 Million Theft Left No Regulator To Call
Bitget blamed North Korea for a $387.5 million wallet-authorization breach, but the exchange sits outside every regulatory perimeter built to catch state-linked crypto theft, so the loss has nowhere official to land.
Sep 20, 2026 · Cyber Intel Column
North Korea's Fake Job Interviews Ran For Eight Months
WaterPlum's fake recruiters drained $10.71 million from 7,000 wallets before four governments named the operation, and the estimated $500 million a year scale suggests most of it is still running.
Sep 13, 2026 · Cyber Intel Column
Check Point's Own Bug, Everyone Else's Deadline
Check Point patched two critical VPN flaws before anyone exploited them, but the manual hotfix APAC banks must run is slower than attackers have historically needed to catch up.
Recent Briefings
Oct 28, 2026 · CYBER INTEL
A shopper returning to a Convertr checkout after its repair could still run the malicious analytics script saved in their browser, according to security firm Sansec. The server-side cleanup has a browser-side remainder. Another payment can still encounter malicious code.…
Read full filing →
Oct 26, 2026 · CYBER INTEL
Gheist uses stolen GitHub tokens to plant workflows that encode repository secrets in base32, print them into GitHub Actions logs, then download the logs and delete the runs.…
Read full filing →
Oct 26, 2026 · CYBER INTEL
Tailscale SSH port forwarding let an ordinary session reach a system socket through a process running as root, according to research published on October 25. The test then obtained root access and read the system password file. No administrator rights were needed at the start.…
Read full filing →
Oct 26, 2026 · CYBER INTEL
A Python client can start decoding Brotli responses because a package is installed, even when the application’s own code never imports it. For the administrator checking that service, searching the source code for Brotli calls can miss the route entirely. The dependency changes the client’s behaviour.…
Read full filing →
The Wang Report's correspondents are authored personas; the work under their bylines is produced by AI under human editorial direction, and their biographical details, including any affiliations, are illustrative rather than literal. How the masthead works.