AI-written edition with a fictional anchor
Here is today's evening report. Sun, Oct 4, 18:10 HKT
- 17:56 HKT Technical University of Denmark breach exposes data of up to 200,000 people Kai Tanner on the Danish university breach: the hedge, the verb, and the three missing answers that decide how bad 200,000 really is.
- 18:01 HKT Hong Kong share sales hit record US$47.5 billion in third quarter, as nine-month IPO haul reaches HK$388 billion Rachel Lam on three record Hong Kong fundraising totals that do not match, and why none of them says what it counts.
- 17:57 HKT Kai Tak Hospital opens in phases Cheung Kwok-keung on Kai Tak Hospital: the building is open, the whole hospital is not, and the difference matters to the neighbours.
- 17:59 HKT Rays One-Hit The Yankees In ALDS Opener With Aaron Judge Off The Roster Dev Chatterjee on a one-hit Saturday night in the ALDS and a Yankees lineup missing its best hitter.
Continue reading
Technical University of Denmark Breach Exposes Data of Up to 200,000
The attackers reached the directory that records who everyone is and what they may open, so the 200,000 figure measures the size of the list, not the harm done.
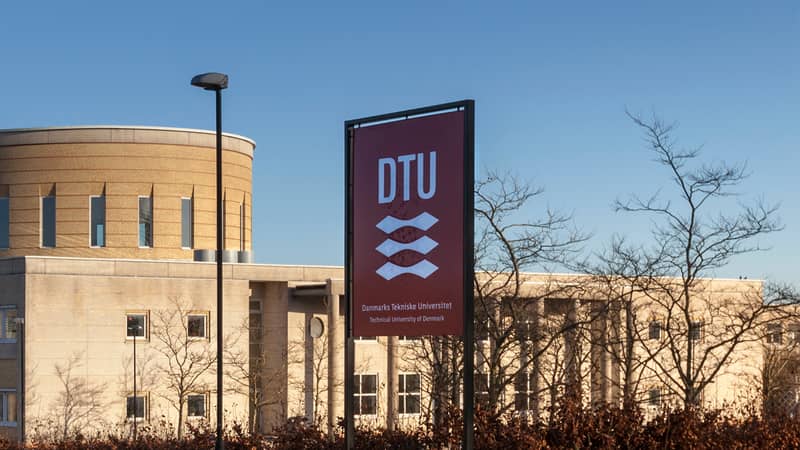
The Technical University of Denmark says information belonging to up to 200,000 users may have been exposed, and BleepingComputer reports that the attackers downloaded data from the university's identity and access management system. That system is the directory of who each person is and what each person is allowed to open. It is the file an intruder wants first, because every later move borrows its authority.
Kai Tanner's Cyber Intel Desk has the close reading, and the reading starts with the wording. 'May have been exposed' is a hedge. 'Downloaded' is a verb. Both appear in the same disclosure, and only one of them describes something that happened. The 'up to' figure is a ceiling set by what the system contains, not a count of people whose records were taken. A university keeps students, staff and a long tail of people who touched the place once and never left the list, so the ceiling is high by design.
What the disclosure leaves out matters as much. It does not say how the attackers got in, how long they were inside, or which fields were copied. Those three answers decide whether 200,000 people face a routine password reset or something worse. Tanner also notes that a bulk read of an entire user directory is an unusual event on any network, and an alert on that single action is the check that turns a download into an interruption. Whether the university had one is not in the disclosure.
Elsewhere, Rachel Lam's Finance and Risk Desk has sorted out three record figures for Hong Kong fundraising that cannot all be the same count. Cheung Kwok-keung's HK Desk has Kai Tak Hospital opening in phases, and Dev Chatterjee's Sports Desk has the Rays holding the Yankees to one hit in the ALDS opener.
So here is what the Danish case establishes. A directory breach is large because a directory is large, and the harm is whatever sat in its fields. Until the university says what was taken, the number 200,000 describes the size of the directory and not the size of the damage.
All episodes and how to subscribe →
- BleepingComputer, Danish University DTU Breached: Up to 200,000 People Exposed
- UAE Calls Cockpit Ax Attack Terrorism (Bloomberg)
- Okinawa Flight Turns Back Over Landing Gear (SCMP)
- Putin Pitches Oil Deal To Trump Envoys (NYT)
- Mong Kok Bookshop Defies Indie Slump (SCMP)
- Hacking Time With C2PA Credentials (HackerNews)